A school district thought it was updating a vendor’s bank details
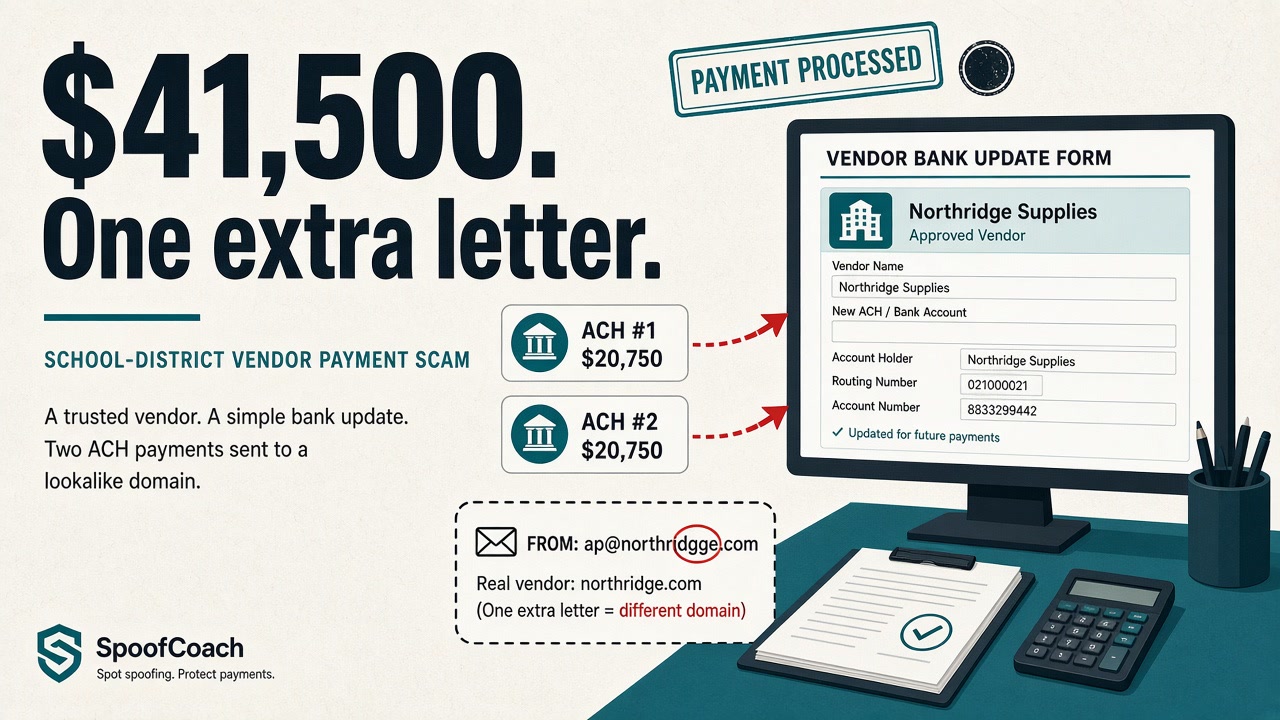
A school district’s finance office thought it was updating a vendor’s bank details.
In October 2024, West Geauga Local Schools in Ohio got email that looked like it came from the owner of a long-time vendor. The message asked for updated ACH info for electronic payments. It had the vendor’s name, logo, and an invoice. The catch was quiet: the sender’s domain had one extra letter. Staff took the updated banking forms at face value and changed the payment path.
Two ACH payments followed — $41,500 total — into accounts controlled by thieves. Investigators chased the money through banks and never recovered a named suspect. Insurance covered most of it. A $5,000 deductible stayed. Ohio’s auditor later dinged the district for skipping state guidance on payment-redirect scams and issued a finding for recovery against the treasurer and accounts-payable specialist for that deductible.
Public money. A domain that looked almost right. One change to “where we pay” without a second channel to confirm.
If you run a public or finance inbox, ask one plain question: can strangers email as your vendors — or as you?
Paste your domain at spoofcoach.com. See if you’re exposed or protected. One next step. Free.